Ransomware Weekly, 1–7 Nov 2026: 53.7M Claimed Henry Pratt Rows, Atomberg and Kirkland & Ellis
Claims indexed 1–7 Nov 2026: Henry Pratt (53.7M rows), Atomberg (8.2M) and Kirkland & Ellis (452K), with domain evidence and attribution limits.
Coming Tuesday: Breaches Weekly. Past editions.
Covers leaks indexed by HaveIBeenRansom between 2026-11-01 00:00 and 2026-11-07 23:59 UTC. Each case shows when it was listed and when its data became searchable. How we pick cases, read records and score attribution: methodology.
Why these three
Henry Pratt, Atomberg and Kirkland & Ellis stand out for different reasons: the scale of a manufacturer-labelled dataset, a dense concentration of repeated organisation-linked strings, and a smaller file set bearing a law firm's name. Together they account for 62,377,561 indexed records across three entries. That is a sum of source records, without cross-source deduplication, not a count of people or new attacks. All three became searchable during 1–7 Nov 2026 according to HaveIBeenRansom metadata. Their extortion listings predate the week.
Henry Pratt's low automated score overlooks a documented relationship with its dominant email domain. Atomberg's high score accompanies repeated strings that cannot be counted as staff mailboxes. Kirkland & Ellis has organisation-linked email observations but no established confirmation of this indexed copy. Suppliers, security teams and affected businesses will need to ask different questions in each case.
| Metric | Henry Pratt | Atomberg | Kirkland & Ellis |
|---|---|---|---|
| Actor / posting channel | Clop | Clop | Silent Ransom Group |
| Listed / post observed (UTC) | 2026-09-10 | 2026-08-12 | 2026-10-22 |
| Indexed (UTC) | 2026-11-03 00:00:45 | 2026-11-02 20:22:01 | 2026-11-02 22:34:07 |
| Records indexed | 53,683,286 | 8,241,790 | 452,485 |
| Records with email | 5,689 | 467,119 | 565 |
| % of records with email | 0.01% | 5.67% | 0.12% |
| Corporate / personal (% of email-bearing records) | 99.86% / 0.14% | 100.00% / 0.00% | 58.41% / 41.59% |
| API attribution heuristic v2.0 | 2/100 (very low) | 100/100 (high) | 69/100 (medium) |
| Incident / exact copy | Unconfirmed / not authenticated | Unconfirmed / not authenticated | Unconfirmed / not authenticated |
Swipe horizontally to read every column. Selected files indexed 1–7 Nov 2026. Posting dates and indexing dates are shown separately. Counts are records, not people.
Key findings
Henry Pratt: 53,683,286 records. Only 5,689 are email-bearing; the volume is not a customer or employee count.
Atomberg: 99.80%. This share of its corporate-classified email-bearing records uses a subdomain the attribution service flags as a repetitive artefact.
Kirkland & Ellis: 452,485 records. Its 565 email-bearing records offer a narrow attribution clue, not an inventory of affected clients.
The table's listing dates are the source-discovery dates recorded by HIBR, not verified intrusion dates. All three incident claims remain unconfirmed in the evidence reviewed. File-type counters overlap and must not be added to produce a new total. The automated attribution scores evaluate 55 available points and leave analyst provenance and external corroboration pending; a displayed 100/100 is not certainty. No raw personal records were inspected for this edition, so specific contents below are limited to aggregate metadata and explicitly attributed claims.
1 · Henry Pratt (listed by Clop)
HIBR entry: Henry Pratt on HaveIBeenRansom
What happened. Clop listed HENRYPRATT.COM in a posting recorded on 10 September 2026. The indexed entry became searchable on 3 November. Henry Pratt's official contact page describes valve-order and technical-support routes and links its business to Mueller domains. That context supports treating this as a relevant manufacturer-labelled dataset; it does not confirm Clop's assertion or a disruption to water infrastructure.
Scale. The entry contains 53,683,286 indexed records, of which 5,689 carry an email observation: 0.01% when rounded to two decimals. The attribution service separately reports 23 distinct addresses on the declared henrypratt.com domain and 24 record occurrences for that domain. Those are different units and cannot explain the entire dataset's population.
What the data contains. The metadata associates 53,683,285 records with CSV sources and one with a database source. It also reports DOC, EML and XML counters, so the file-type categories are non-additive. The file counter reports 312 CSV sources. These measures describe ingestion formats; they do not establish that the contents are customer lists, engineering drawings or operational credentials. The automatically generated company description is not treated as evidence of file contents or ownership.
Corporate vs Personal. muellerwp.com accounts for 85.87% of the corporate-classified bucket. Henry Pratt's own contact page directs valve-order and service enquiries to that domain. The automated model's treatment of it as a dominant third party therefore needs qualification. This relationship explains why the low score should not be read as a finding that the claimed origin is false; it still cannot authenticate this particular file set.
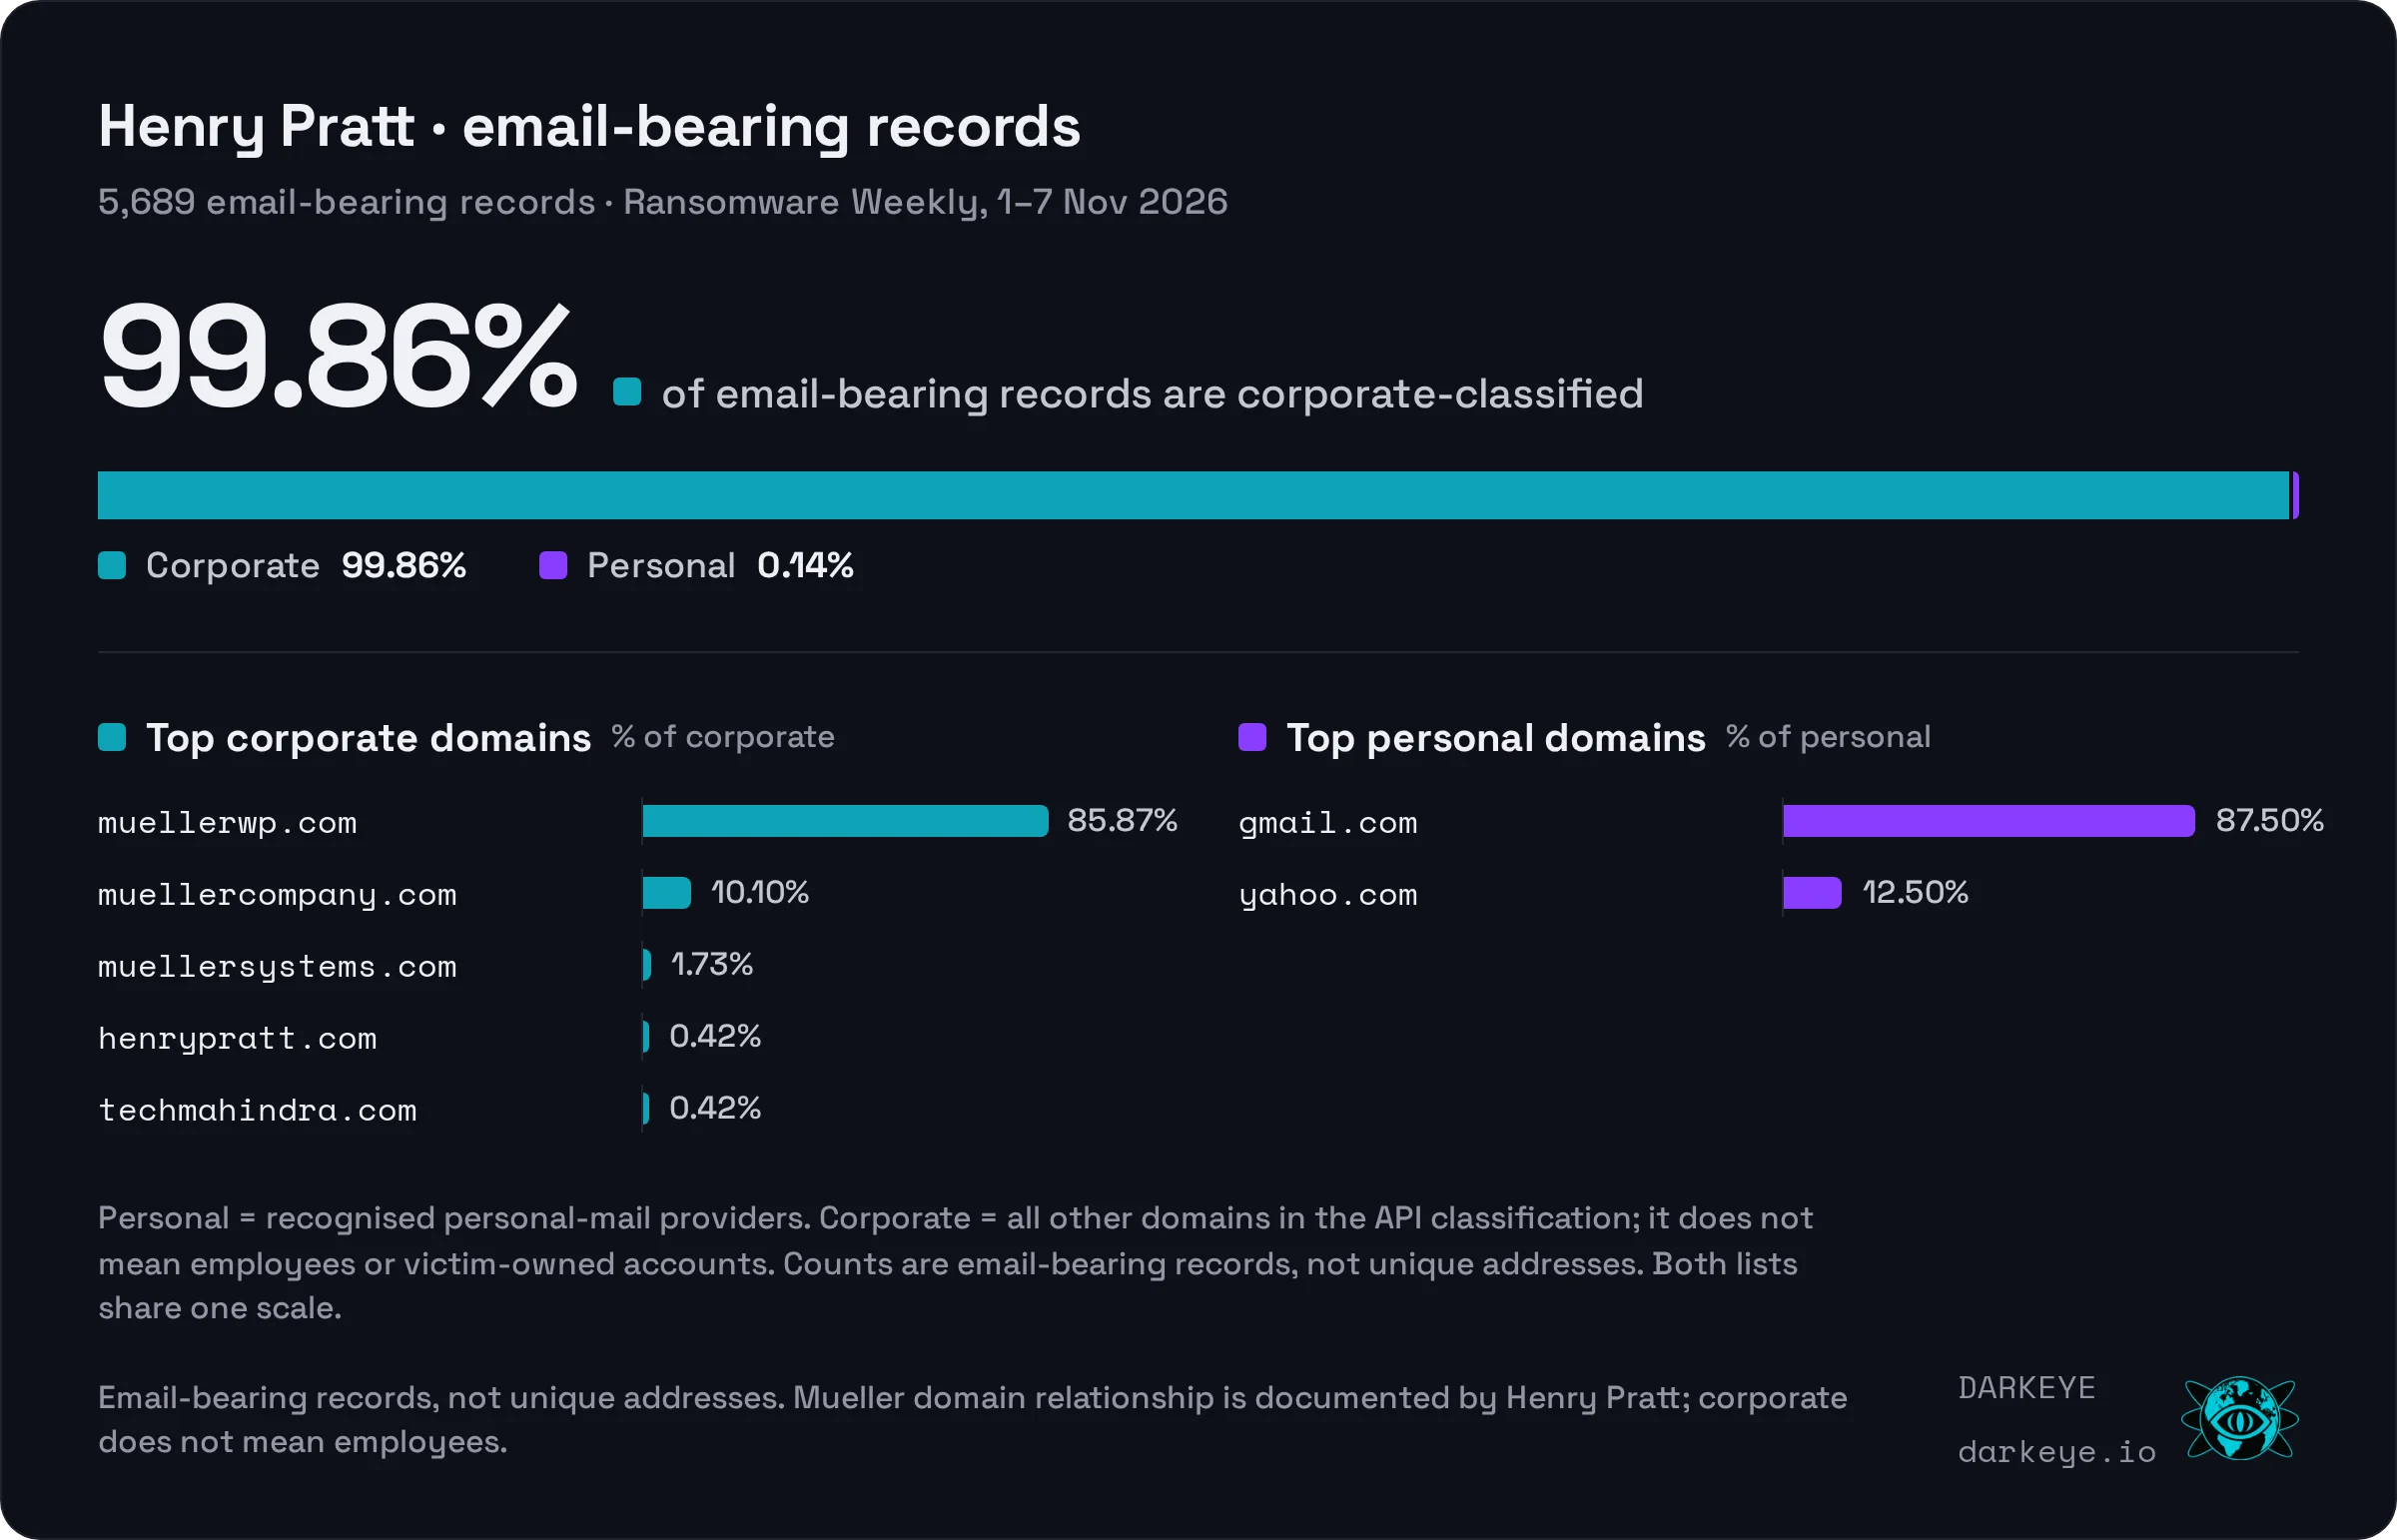 Email-bearing records, not unique addresses. Mueller domain relationship is documented by Henry Pratt; corporate does not mean employees. Source: HIBR entry.
Corporate-classified: 5,681 (99.86%); personal-provider: 8 (0.14%). Denominator: 5,689 email-bearing records, not deduplicated people or mailboxes. Corporate means the API's non-personal-provider bucket, not employees or ownership. Each table uses its own bucket as denominator.
| Corporate-classified domain | % of its bucket |
|---|---|
| muellerwp.com | 85.87% |
| muellercompany.com | 10.10% |
| muellersystems.com | 1.73% |
| henrypratt.com | 0.42% |
| techmahindra.com | 0.42% |
| Personal-provider domain | % of its bucket |
|---|---|
| gmail.com | 87.50% |
| yahoo.com | 12.50% |
Attribution confidence: 2/100 (very low). This is the API's unmodified score: one raw point normalised over 55 evaluated points after a 15-point third-party penalty. It is not a 2% probability. Analyst assessment: likely related to the Henry Pratt/Mueller business context, with moderate confidence, because the domain relationship is independently documented. A matching corporate disclosure or verified provenance for the files would strengthen the link; conflicting source provenance would weaken it. The numerical score remains unchanged.
Why it stands out this week. It has the largest record count among the selected cases. Interpreting its automated attribution score requires the documented contact-domain relationship. Treat its size as an investigation priority, not a measure of confirmed harm.
2 · Atomberg (listed by Clop)
HIBR entry: Atomberg on HaveIBeenRansom
What happened. Clop's Atomberg listing is dated 12 August in HIBR's source metadata, with indexation on 2 November. The retained posting claims databases and project files. Atomberg's official site identifies its consumer-appliance business. That gives the name context without verifying the file claim. No evidence reviewed establishes encryption, an outage or a particular access route.
Scale. HIBR counts 8,241,790 records and 467,119 email-bearing records, or 5.67%. The latter should not be reported as 467,119 staff accounts: the attribution service identifies only 393 distinct corporate address-like values, including 392 on the declared organisation domain and its subdomains, and explicitly flags repetition.
What the data contains. The posting claims database and project material, while the file metadata classifies 8,241,790 records under CSV and records 236 CSV source files. Separate DOC and XML counters also appear and are not additive to that total. The domain label plmprod.atomberg.com occurs prominently in the email-origin output, but the label alone cannot prove that product designs, a live application or its credentials are exposed. No field names from raw records are asserted here.
Corporate vs Personal. The API assigns the whole email-bearing bucket to corporate classification, with 99.80% under plmprod.atomberg.com. Its own attribution factors mark that subdomain as a repetitive artefact. The table also preserves a file-like parsed domain, 2.5axlsx.xlsx, which further illustrates why an extraction result is not automatically a real mailbox. Neither a 100% corporate split nor an organisation-branded string measures the number of employees affected.
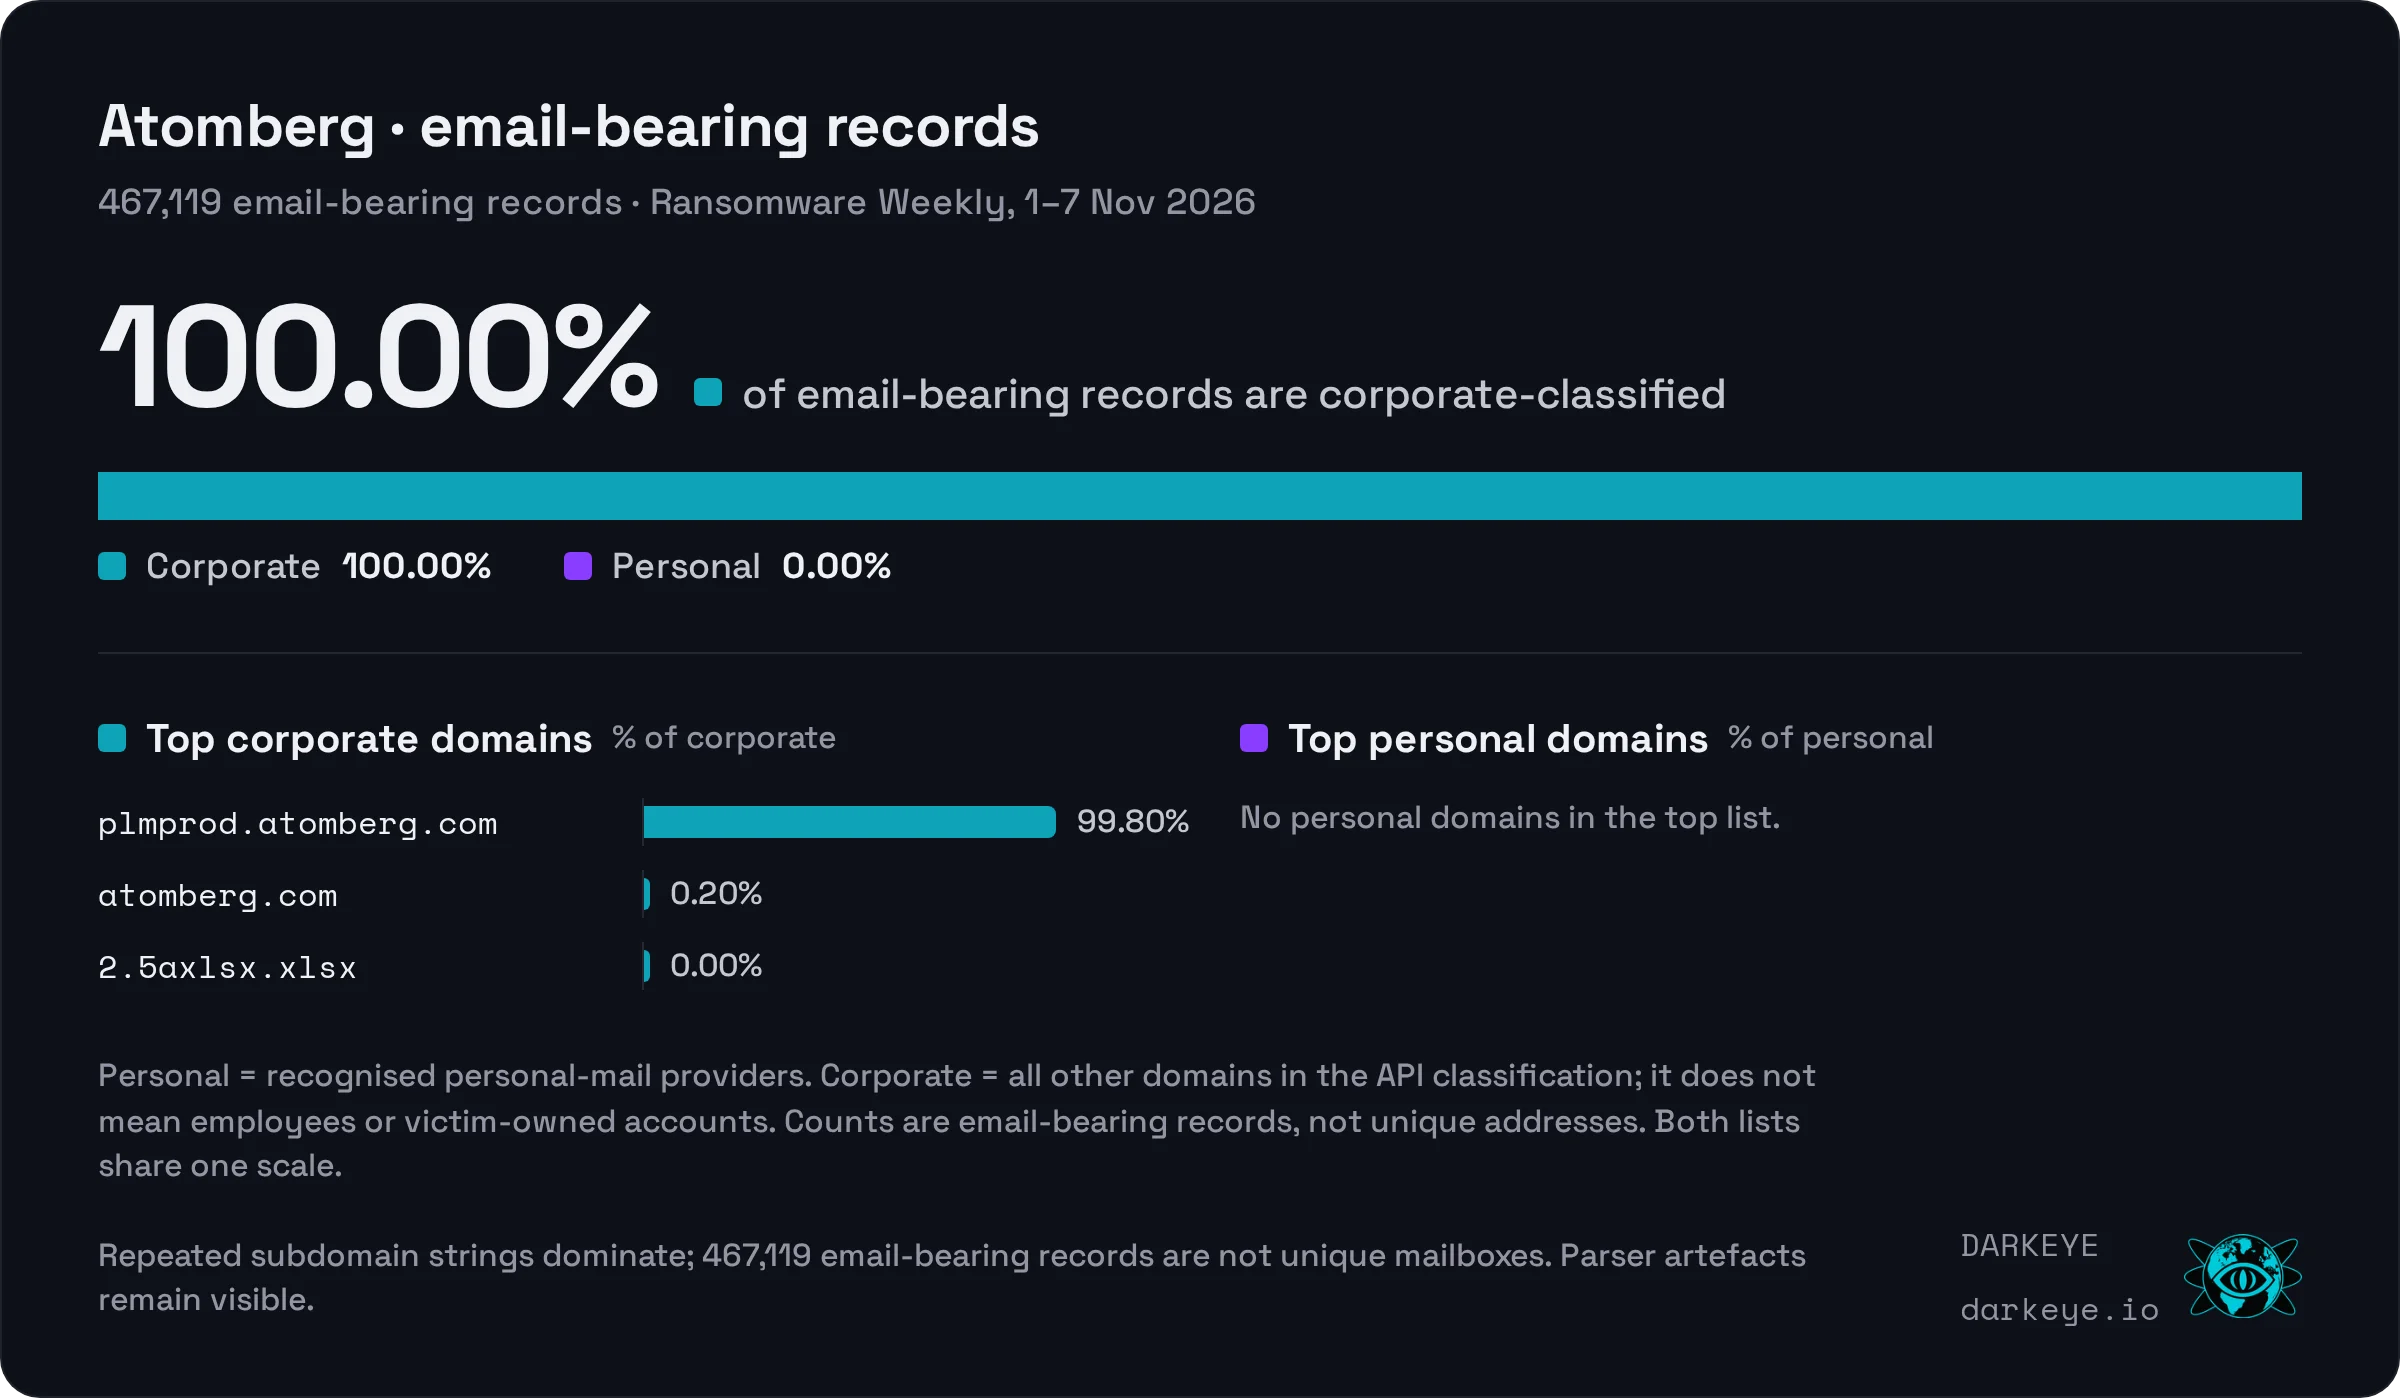 Repeated subdomain strings dominate; 467,119 email-bearing records are not unique mailboxes. Parser artefacts remain visible. Source: HIBR entry.
Corporate-classified: 467,119 (100.00%); personal-provider: 0 (0.00%). Denominator: 467,119 email-bearing records, not deduplicated people or mailboxes. Corporate means the API's non-personal-provider bucket, not employees or ownership. Each table uses its own bucket as denominator.
| Corporate-classified domain | % of its bucket |
|---|---|
| plmprod.atomberg.com | 99.80% |
| atomberg.com | 0.20% |
| 2.5axlsx.xlsx | 0.00% |
| Personal-provider domain | % of its bucket |
|---|---|
| No domains in this bucket | — |
Attribution confidence: 100/100 (high). The displayed 100/100 reflects 55 out of 55 evaluated points, driven by domain and name matches. Analyst-curated provenance and independent corroboration are pending. Analyst assessment: an organisational connection is likely, with moderate confidence, based on the declared-domain matches; authentication of the copy and the circumstances of collection remain unresolved. A verified internal source-file match would help; evidence of synthetic or copied application strings would reduce confidence.
Why it stands out this week. Repeated technical strings dominate the email-bearing total in this case. The aggregate is useful for locating material to investigate, but unsuitable for estimating the people at risk.
3 · Kirkland & Ellis (listed by Silent Ransom Group)
HIBR entry: Kirkland & Ellis on HaveIBeenRansom
What happened. Silent Ransom Group listed Kirkland & Ellis in the source record dated 22 October. HIBR indexed the associated entry on 2 November. The firm's own site establishes the name and legal-services context. No organisation statement in the evidence reviewed authenticates this specific indexed copy. A listing alone cannot establish what happened inside the firm.
Scale. The indexed entry holds 452,485 records, including 565 email-bearing records, or 0.12%. Only 330 fall in the corporate-classified bucket. This small slice is useful for testing the dataset label, but it cannot describe the full population of affected lawyers, clients or matters.
What the data contains. The file metadata reports 451,960 CSV-associated records and 451,398 XLS-associated records, alongside smaller database, mailbox, text and XLSX counters. Their overlap prevents summing them into a larger leak. The mailbox category is a format signal, not proof of a complete email archive. The aggregate metadata does not identify privileged advice, litigation material or financial records, and the fact that the named organisation is a law firm does not establish their presence.
Corporate vs Personal. kirkland.com contributes 35.15% of the corporate-classified records. The attribution service separately reports 114 distinct organisation-domain addresses and 116 record occurrences. Other domains in the table provide context, but their presence does not establish a client relationship or compromise of those organisations.
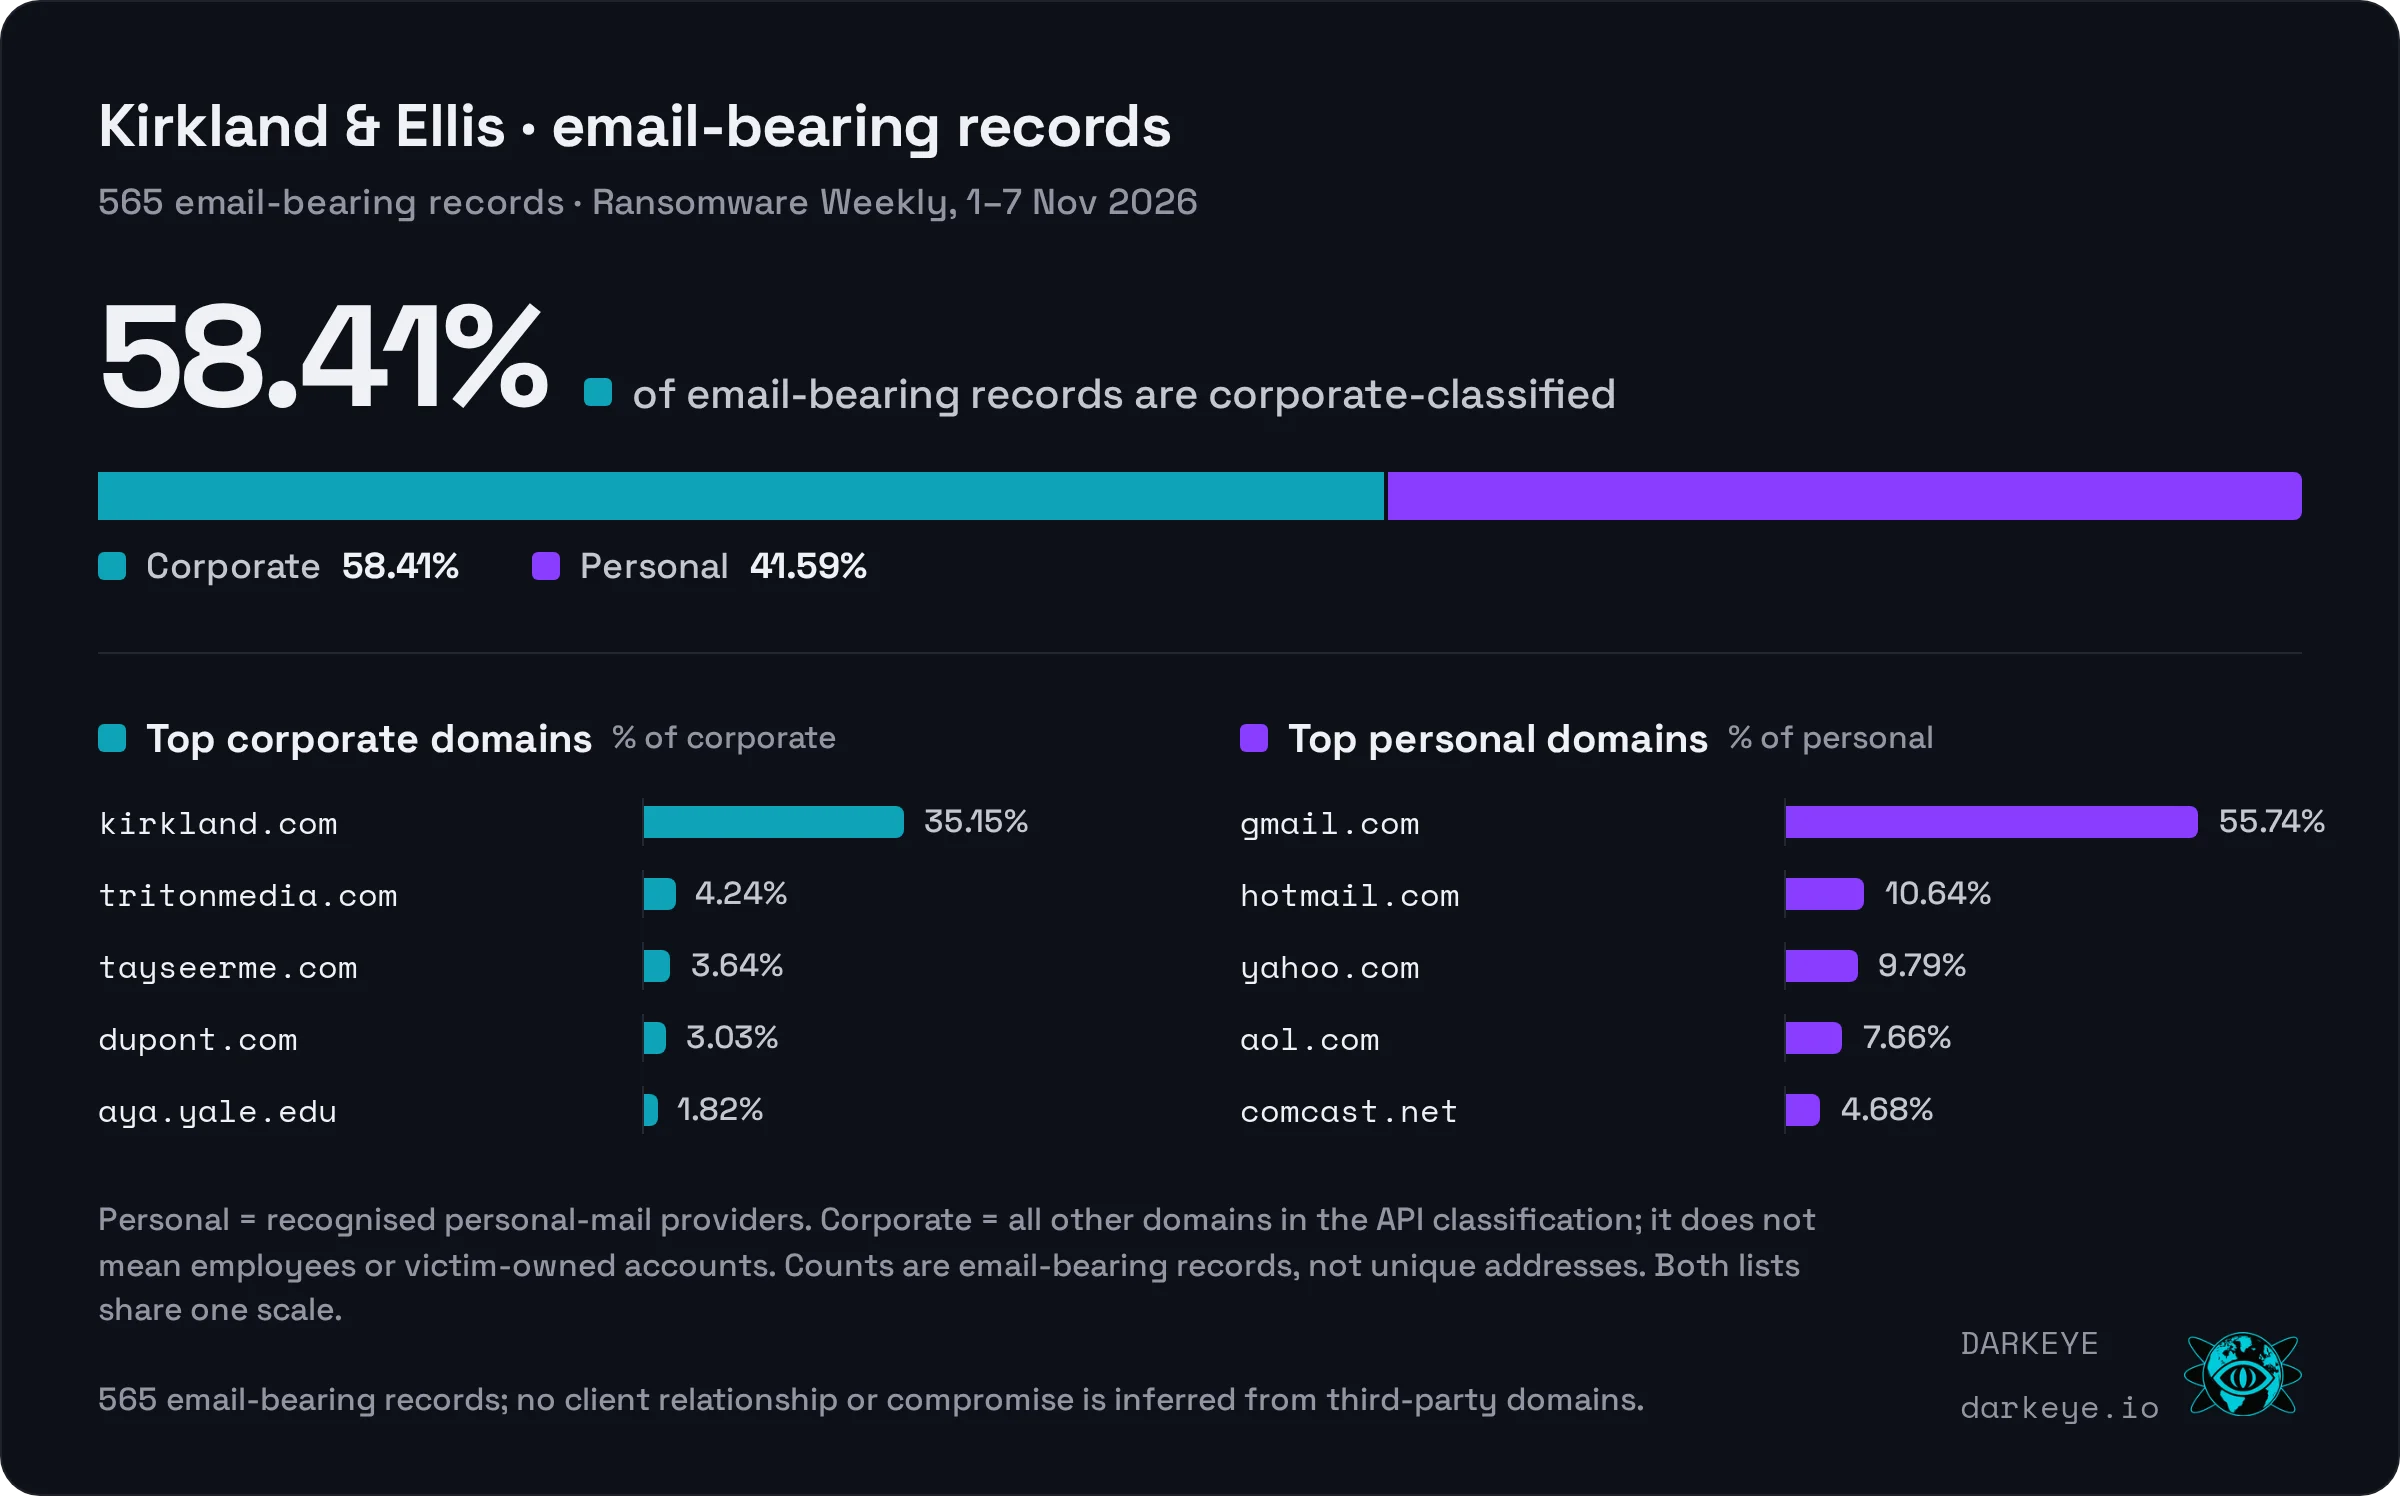 565 email-bearing records; no client relationship or compromise is inferred from third-party domains. Source: HIBR entry.
Corporate-classified: 330 (58.41%); personal-provider: 235 (41.59%). Denominator: 565 email-bearing records, not deduplicated people or mailboxes. Corporate means the API's non-personal-provider bucket, not employees or ownership. Each table uses its own bucket as denominator.
| Corporate-classified domain | % of its bucket |
|---|---|
| kirkland.com | 35.15% |
| tritonmedia.com | 4.24% |
| tayseerme.com | 3.64% |
| dupont.com | 3.03% |
| aya.yale.edu | 1.82% |
| Personal-provider domain | % of its bucket |
|---|---|
| gmail.com | 55.74% |
| hotmail.com | 10.64% |
| yahoo.com | 9.79% |
| aol.com | 7.66% |
| comcast.net | 4.68% |
Attribution confidence: 69/100 (medium). The API returns 38 raw points out of 55 evaluated, normalised to 69/100. Analyst assessment: a connection to the named organisation is likely, with moderate confidence, based on domain and label observations. That assessment is narrower than confirming the actor's intrusion claim. Independent verification of the file provenance or a statement tying this exact copy to an incident would change the assessment materially.
Why it stands out this week. The smaller total still warrants attention because of the named legal-services organisation and the organisation-linked records. Defenders should prioritise the authenticity of any matter-related contact over a ranking based only on dataset size.
What they have in common
- Two Clop listings dominate this selection by indexed volume, but neither the shared group label nor CSV-heavy ingestion establishes a common intrusion or software vulnerability.
- The three email-bearing shares are small relative to their total records. At Atomberg, repeated strings further weaken any attempt to translate that measure into people.
- Domain context changes interpretation: Mueller is documented in Henry Pratt's own contact information, while Kirkland's third-party domains cannot establish client relationships or other victims.
What defenders can do
For teams handling Henry Pratt or Mueller business, verify order and payment changes through an existing contact route. The organisation's own site connects the names; a message using either brand can therefore look plausible. Preserve suspicious messages and compare them with known correspondence. The dataset does not establish that any fraudulent message has been sent.
For Atomberg-related investigations, separate recurring application strings from usable identities. Start with validated account inventories and audit records before deciding which credentials require action. Review access to the repositories implicated by internal evidence, if any; the public subdomain label alone does not identify an exposed service or an intrusion path. Do not convert the 467,119 email-bearing record count into an account-reset list.
For legal teams working with Kirkland & Ellis, verify unexpected document-sharing and matter-related requests with the firm through established channels. An email domain appearing in a file set is not confirmation that its owner is a client or that a matter was disclosed. Escalate corroborated evidence through the organisation's incident-response and legal teams rather than circulating alleged case files.
These actions fit the access-control, logging and incident-response principles in the joint CISA #StopRansomware guide. These metadata establish no case-specific initial-access technique, encryption event or recovery requirement.
Is your company — or one of your suppliers — in a ransomware leak? Search HaveIBeenRansom for free · Monitor your domains with HIBR for business
DarkEye Threat Research · Data: HaveIBeenRansom · Indexing methodology peer-reviewed in MDPI Electronics · Attribution confidence is a heuristic estimate (method v2.0), not a formal attribution.
Spotted an error, or represent an organisation named here? Send us a correction and we will add it to the post.
Darkeye Research Team
JuanmaTracking ransomware crews, breach disclosures and the tooling that matters — field notes from the Darkeye desk.
Intel briefing
Get breach reports before they trend
Ransomware intel and breach disclosures in your inbox. Signal only, no noise.
Read next //
Ransomware Weekly, 25–31 Oct 2026: 21.3M Claimed Pitney Bowes Rows, AngMar and Omni Tanker
Indexed 25–31 Oct 2026: 21.3M Pitney Bowes-labelled rows, 10.6M claimed AngMar records and 1.8M claimed Omni Tanker records, with attribution limits.
Keep investigating //
Discussion (0)
Sign in to join the discussion
Share your take with the Darkeye community.
No comments yet. Be the first to weigh in.