Ransomware Weekly, 18–24 Oct 2026: 282M MAG Rows, Clop Lists 65.8M Thermos Records
Leaks indexed 18–24 Oct 2026: MAG-labelled rows (282M), Clop's Thermos claim (65.8M), Goodwill (27.3M) and SE Oklahoma State (9.2M).
Ransomware Weekly, 18–24 Oct 2026: 282M MAG Rows, Clop Lists 65.8M Thermos Records
Also this week: Breaches Weekly, 18–24 Oct 2026: 9.5M Lalafo Records, Claimed Samsung Defect Lists and 2.7M METRO Rows.
Covers leaks indexed by HaveIBeenRansom between 2026-10-18 00:00 and 2026-10-24 23:59 UTC. Each case shows when it was listed and when its data became searchable. How we pick cases, read records and score attribution: methodology.
Why these four
We selected four datasets that became searchable this week: three extortion listings and a MAG-labelled file included on an assessed link to an extortion claim. The largest is a 282,201,946-row file labelled Manchester Airports Group (MAG) and Stansted. It was posted on Telegram. Its inclusion here rests on a hypothesis linking it to FulcrumSec's MAG claim (moderate analytic confidence); that file-level link is unverified. It is the only one of the four where the organisation itself has confirmed a data theft. Clop's Thermos listing adds 65,759,742 rows. The sampled source-table names point to PTC Windchill engineering software. Interlock's Goodwill listing (27,291,956 records) names one Goodwill affiliate, but the data points to another. Interlock's Southeastern Oklahoma State University listing is the smallest by rows but holds 1,593,605 email-bearing records from student systems.
Last week's Breaches Weekly carried a Manchester-labelled MAG file from the same Telegram channel. The series keeps extortion data in Ransomware Weekly when a forum or channel re-shares it. We apply that rule provisionally to this MAG-labelled file, based on the hypothesised FulcrumSec link described above, not a verified match to the group's dataset.
| Manchester Airports Group | Thermos | Goodwill | Southeastern Oklahoma State University | |
|---|---|---|---|---|
| Actor | FulcrumSec (claim; file link unverified); posted by Database World ROC | Clop | Interlock | Interlock |
| Listed or posted on | 2026-09-02 (Telegram post) | 2026-08-12 | 2026-03-26 | 2026-08-19 |
| Indexed on (UTC) | 2026-10-18 | 2026-10-20 | 2026-10-23 | 2026-10-18 |
| Records indexed | 282,201,946 | 65,759,742 | 27,291,956 | 9,249,476 |
| % of records with email | >99.99% | 0.0002% | 0.42% | 17.23% |
| Corporate / personal email | 16.96% / 83.04% | 100% / 0% | 51.93% / 48.07% | 66.16% / 33.84% |
| Attribution confidence | 27/100 (low) | 100/100 (high) | 27/100 (low) | 100/100 (high) |
| Incident confirmed by the organisation | Yes (data theft, 27 Aug 2026) | No | No | Cyber incident acknowledged; claim not confirmed |
Key findings
| #1 | #2 | #3 |
|---|---|---|
| 282,201,946 indexed rows; 1,000 sampled events The 1,000 MAG-labelled records examined were email-engagement events. This sample does not characterise all indexed rows or explain their relationship to the 8.7 million affected customers reported by BleepingComputer. |
103 email-bearing Thermos records The Thermos source tables carry PTC Windchill names, which fits Clop's PLM-focused campaign. |
0 records for the listed Goodwill domain The post names a Pennsylvania affiliate, but the corporate email in the data centres on Goodwill of Greater Grand Rapids. |
None of this week's attribution scores includes the analyst-curated factors (data nature and external corroboration), so 55 of 100 points were evaluable in each case. Record readings are domain-filtered slices, not representative samples of each complete dataset.
1 · Manchester Airports Group (listed by FulcrumSec)
HIBR entry: Manchester Airports Group on HaveIBeenRansom
What happened. On 27 August 2026 MAG, which operates Manchester, London Stansted and East Midlands airports, disclosed that an unauthorised third party had stolen customer data from car park, lounge, Fast Track and airport Wi-Fi services. FulcrumSec claimed the theft and told BleepingComputer that it got in with airport-specific Iterable API credentials exposed in client-side JavaScript, then published the data on its leak site. A file named for MAG and Stansted appeared on the Database World ROC Telegram channel on 2 September; HIBR indexed it on 18 October.
Scale. HIBR indexed 282,201,946 records from 21 JSON files, and 282,201,283 of them carry an email address. BleepingComputer reported about 8.7 million affected customers: these rows are not people.
What the data contains. We read the context of 1,000 records in the gmail.com slice. All came from one source, an events_emailOpen export. In the 500 we profiled field by field, every record carries a creation timestamp, campaign, template, message and content identifiers, an IP address, a user agent and a bot flag; 93.8% carry a user ID and 52.8% a country. Every date in the 1,000 records falls in 2025, the latest on 21 August 2025. These event dates do not establish when the data was taken. This is engagement telemetry from an email-marketing platform, the kind of data an Iterable account holds. It matches the "customer-engagement data" in FulcrumSec's samples. We saw no booking or parking records in that slice; it cannot show whether they exist elsewhere in the file.
Corporate vs Personal. Personal mailboxes account for 83.04% of email-bearing records and corporate domains for 16.96%. The corporate class is mostly UK internet-provider mailboxes, which in practice are often household addresses, plus milledmail.com, a newsletter-archiving service whose addresses subscribe to retail mailing lists.
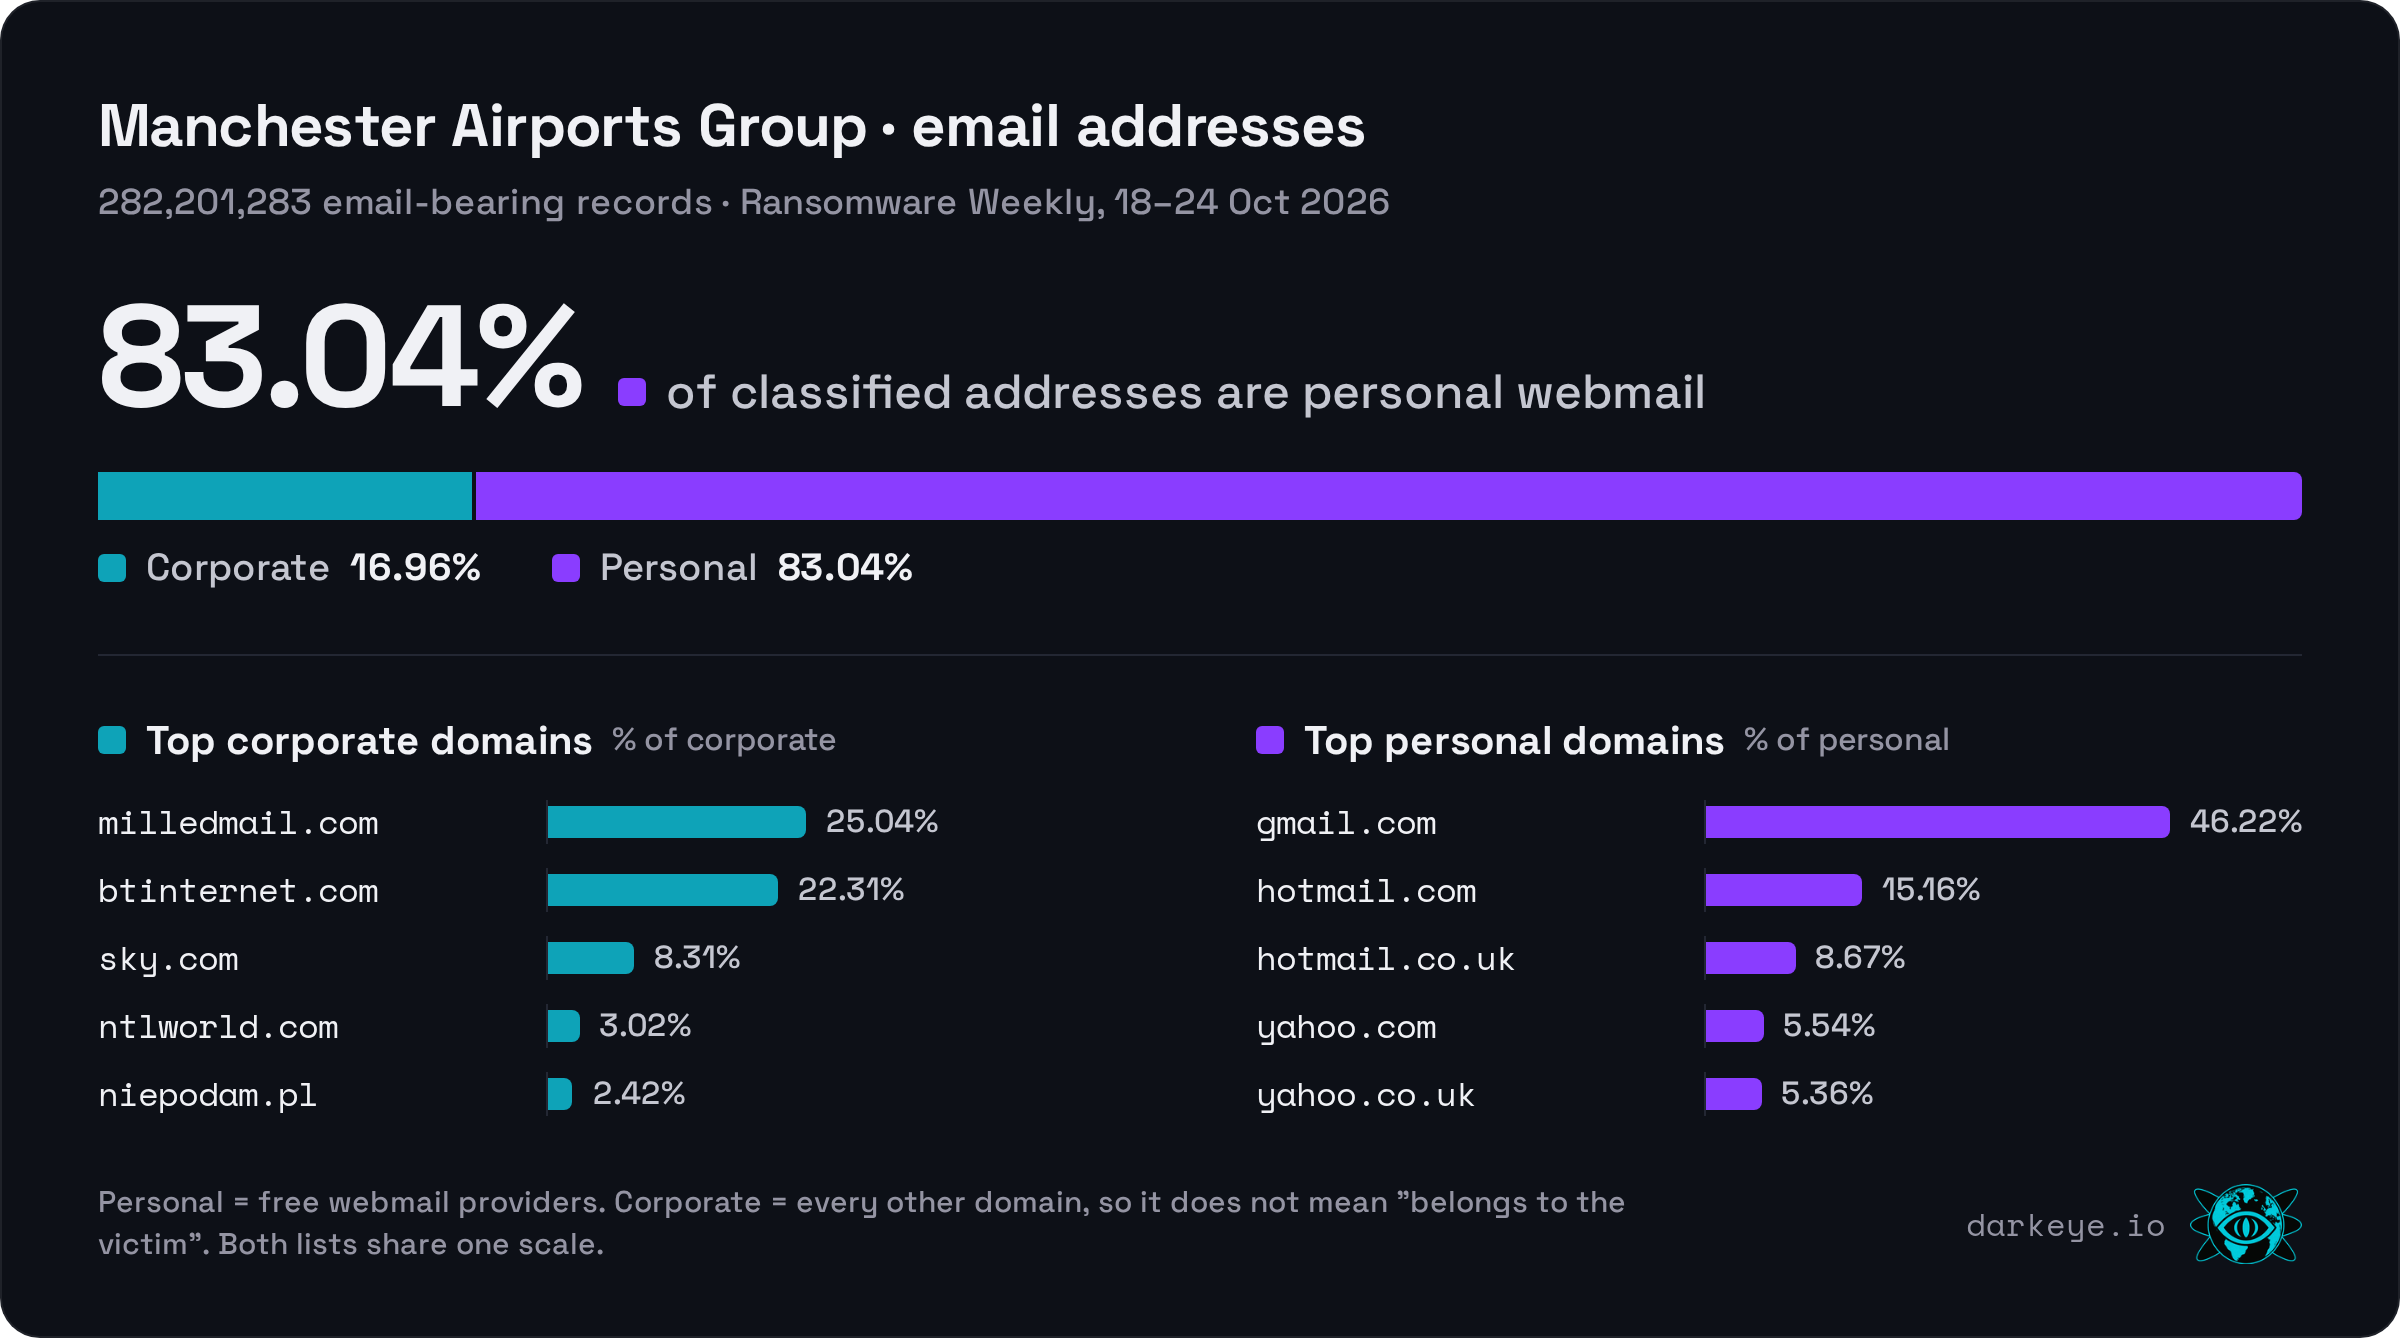
| Corporate domain | % of corporate | Personal domain | % of personal |
|---|---|---|---|
| milledmail.com | 25.04% | gmail.com | 46.22% |
| btinternet.com | 22.31% | hotmail.com | 15.16% |
| sky.com | 8.31% | hotmail.co.uk | 8.67% |
| ntlworld.com | 3.02% | yahoo.com | 5.54% |
| niepodam.pl | 2.42% | yahoo.co.uk | 5.36% |
Attribution confidence: 27/100 (low). The low score comes from how the file name was parsed: stansted.tar was treated as the organisation domain, so the email-domain factor matched nothing. Content labels earned 15 of 15. MAG's confirmation is not part of the automated score; 27 does not express doubt about the confirmed MAG breach. Whether this specific file is FulcrumSec's dataset is not verified. Hypothesis, not fact: the file labels and sampled schema are consistent with a link to FulcrumSec's claim (moderate analytic confidence). The event dates do not establish that link.
Why it stands out this week. This is the largest dataset indexed this week. MAG has confirmed a data theft; the link to this specific file remains unverified. The sampled events connect email addresses with device and location metadata. The API-key entry route remains an actor claim.
2 · Thermos (listed by Clop)
HIBR entry: Thermos on HaveIBeenRansom
What happened. Clop listed THERMOS.COM on 12 August, claiming 285 GB of "Database, Projects, Soft installers". HIBR indexed the data on 20 October. PTC confirms CVE-2026-12569 affects Windchill and FlexPLM. That advisory does not establish how the Thermos data was obtained; no company statement was found in the earlier review.
Scale. 65,759,742 total records. Separate file-type counts: CSV 65,759,742, documents 50,619, XML 4,815. These do not reconcile with the total and must not be added. Only 103 records contain an email address.
What the data contains. We read the thermos.com-domain records HIBR returned. Most come from a table export named WTUser; the rest come from Cabinet, PInstanceDeleteRecord and PreferenceDefinition. PTC documentation identifies WTUser as its Windchill user class. The dates in those records run from 2013 to 24 June 2026. Hypothesis, not fact: a Windchill database export is likely (moderate analytic confidence); the exploit used is unknown. No identity documents were classified.
Corporate vs Personal. All 103 email-bearing records are corporate. No personal mailbox appears.
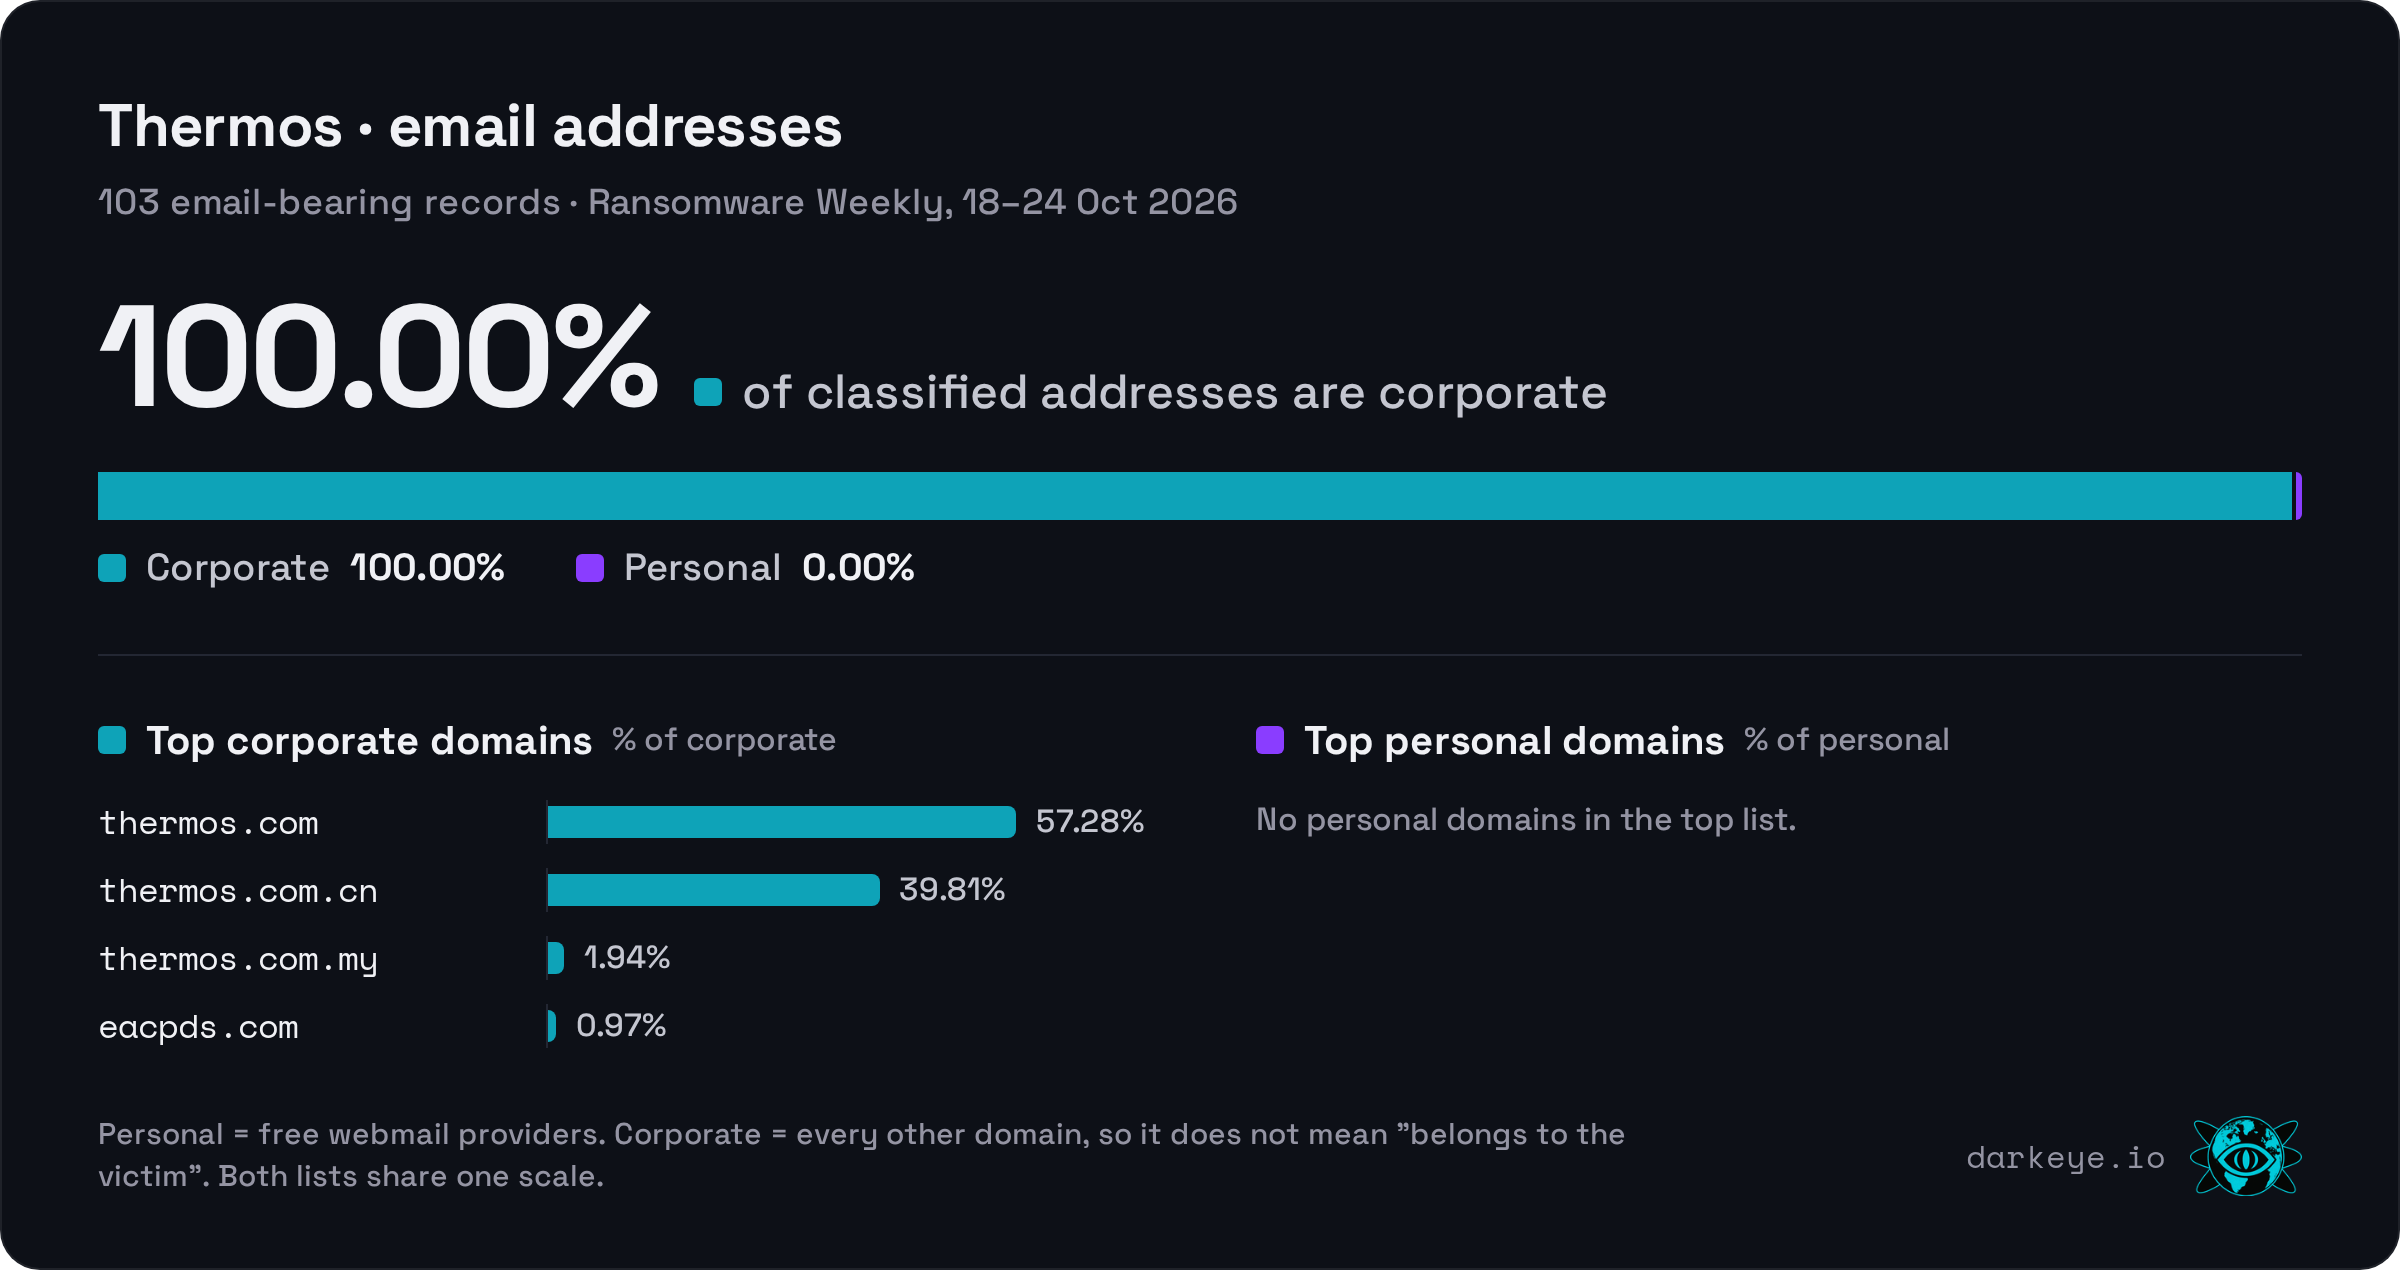
| Corporate domain | % of corporate |
|---|---|
| thermos.com | 57.28% |
| thermos.com.cn | 39.81% |
| thermos.com.my | 1.94% |
| eacpds.com | 0.97% |
eacpds.com belongs to EAC Product Development Solutions, a long-standing PTC reseller and Windchill services partner. A partner domain in a PLM user table is expected and does not show the intrusion vector.
Attribution confidence: 100/100 (high). The declared domain is the top corporate domain (40 of 40 points), and organisation labels appear in the content (15 of 15).
Why it stands out this week. The sampled account tables make partner-access review relevant. Their presence does not establish that designs or other PLM content are in this file.
3 · Goodwill (listed by Interlock)
HIBR entry: Goodwill on HaveIBeenRansom
What happened. Interlock listed "Goodwill" on 26 March 2026. The post describes Goodwill Industries of North Central Pennsylvania and gives goodwillinc.org as the website. HIBR indexed 27,291,956 records on 23 October. DysruptionHub reported that a document in Interlock's own post named Goodwill Industries of Greater Grand Rapids, a Michigan affiliate that disclosed a cyber incident and cash-only stores in March 2026. Neither organisation has confirmed data theft.
Scale. HIBR's non-additive file-type counters report 26,430,952 JSON records from 301 files, 600,972 CSV rows from 3,060 files, 665,378 spreadsheet rows from 2,291 files, 543 database records from 348 files, and smaller document, PDF and text sets. 113,407 records contain an email address.
What the data contains. In the goodwillgr.org records we read, the sources are mail-gateway message logs (subject, action, source IP, whitelisting), facilities maintenance tickets with a "Goodwill Location" field, Exchange server application logs, and MSSQL tables named FlattenedEmployee and AD, which point to HR and directory exports. A query for the listed domain, goodwillinc.org, returned no records.
Corporate vs Personal. Corporate addresses make up 51.93% of email-bearing records and personal addresses 48.07%.
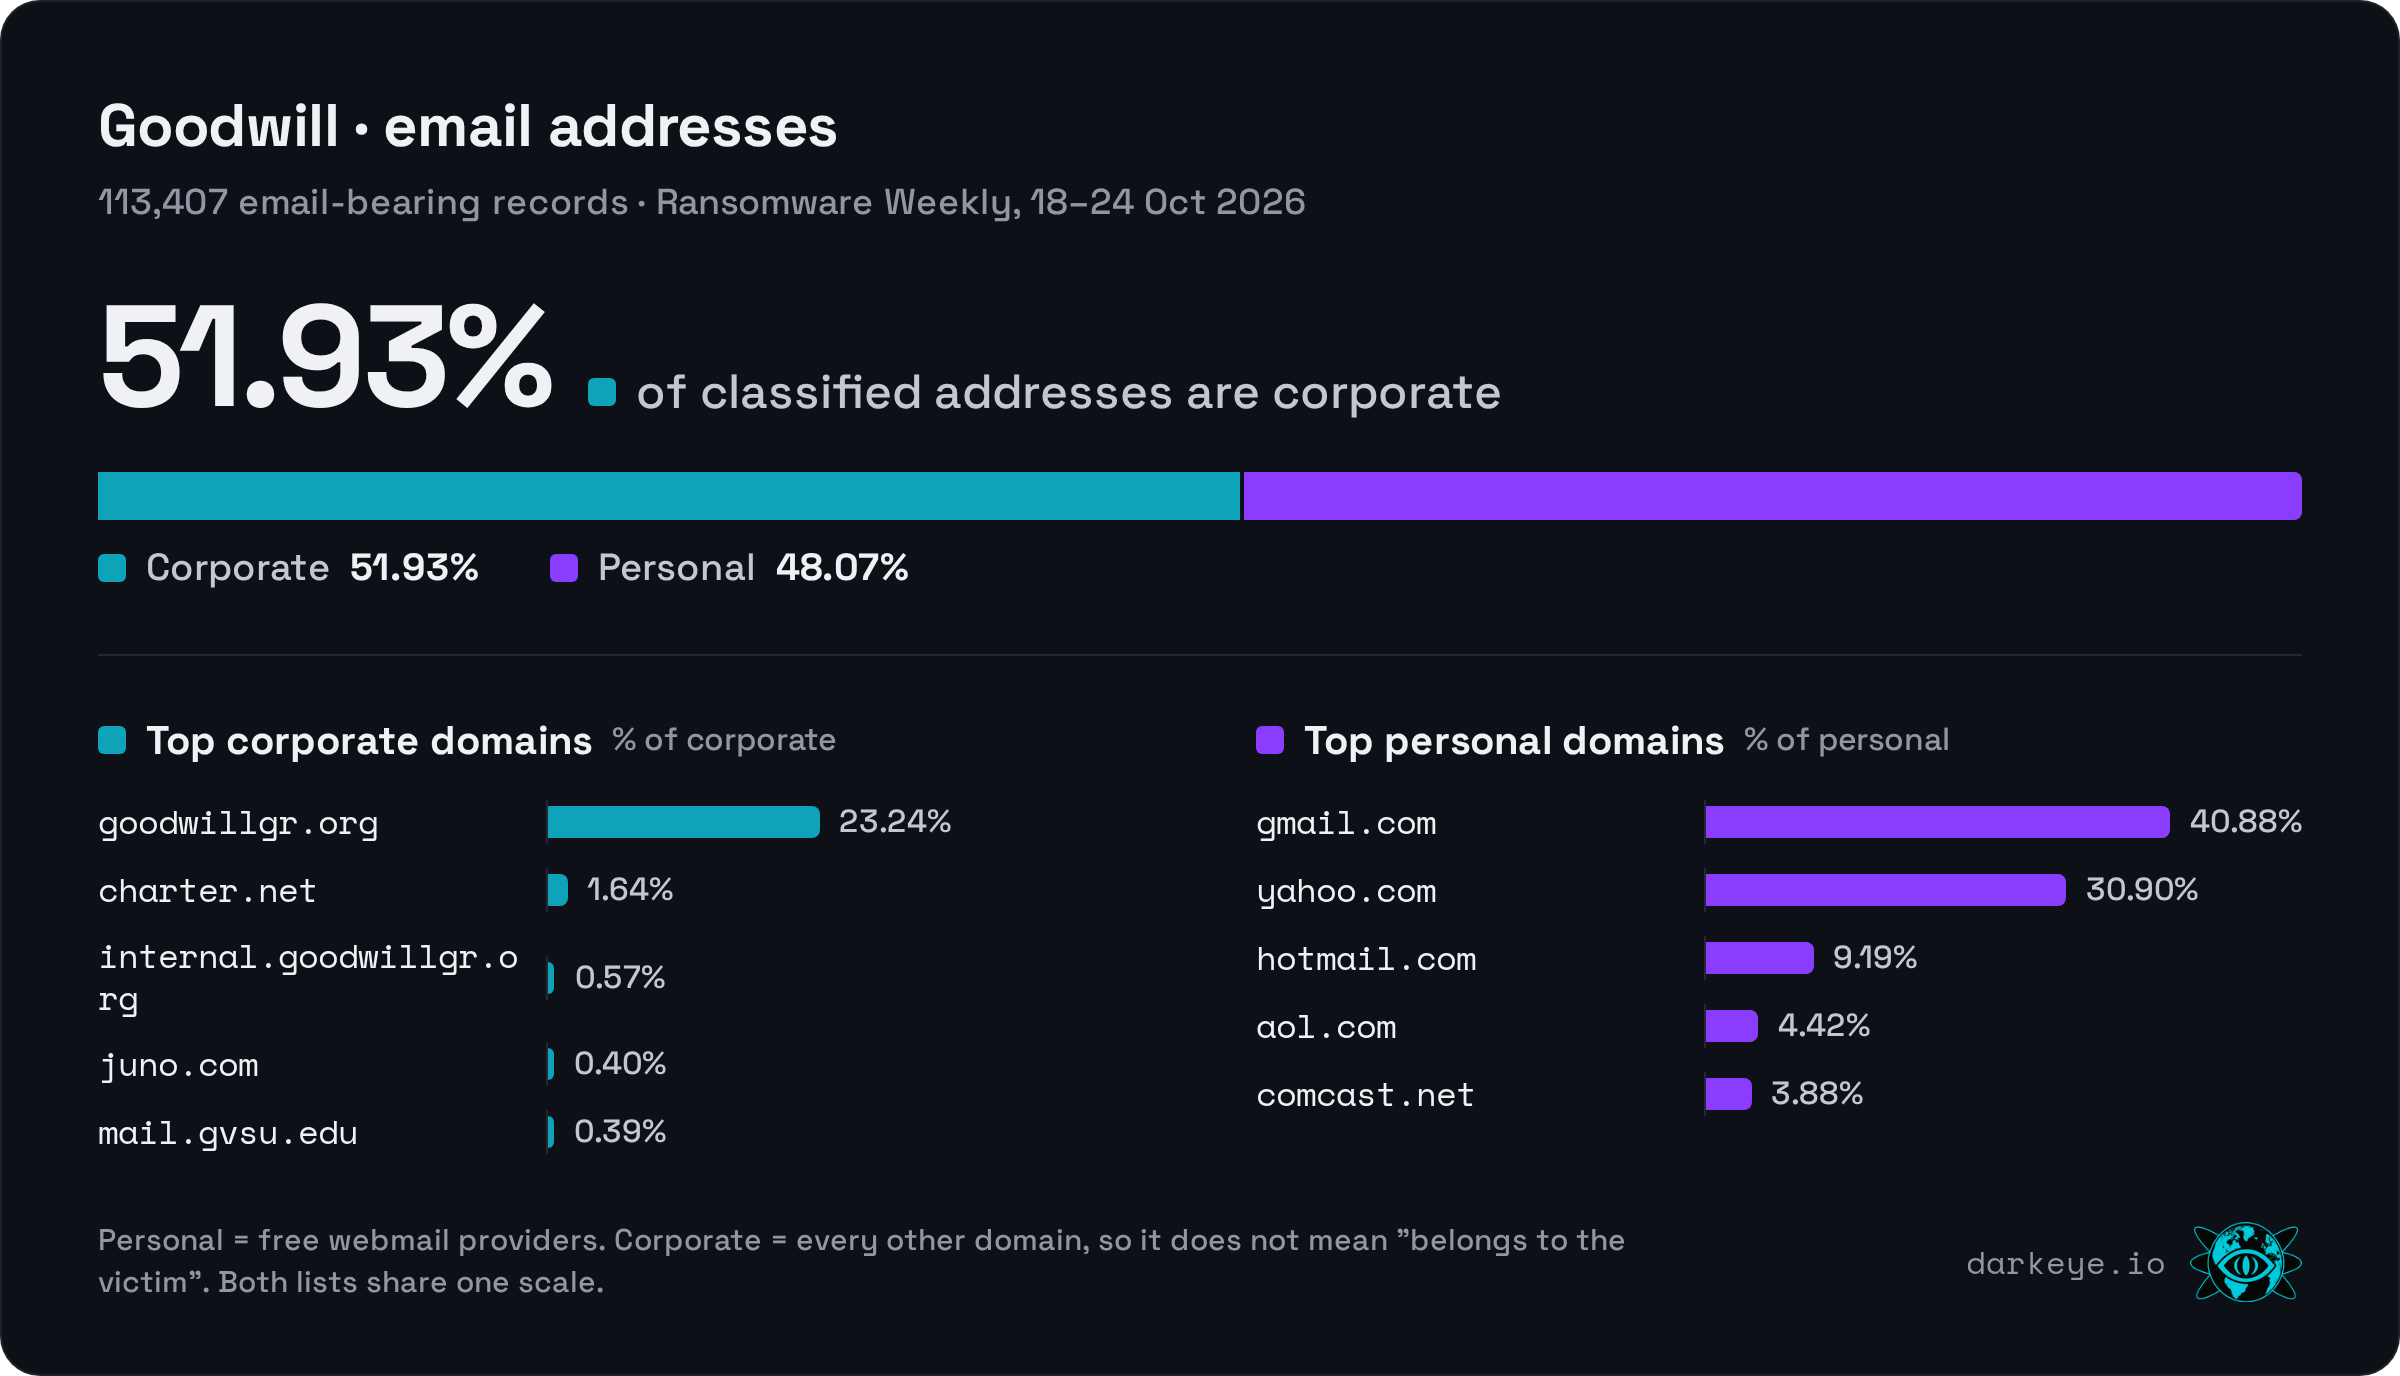
| Corporate domain | % of corporate | Personal domain | % of personal |
|---|---|---|---|
| goodwillgr.org | 23.24% | gmail.com | 40.88% |
| charter.net | 1.64% | yahoo.com | 30.90% |
| internal.goodwillgr.org | 0.57% | hotmail.com | 9.19% |
| juno.com | 0.40% | aol.com | 4.42% |
| mail.gvsu.edu | 0.39% | comcast.net | 3.88% |
Attribution confidence: 27/100 (low). The score was computed against goodwill.org, inferred from the name "Goodwill". That domain appears only 26 times, and the concentration of goodwillgr.org triggered an 8-point third-party penalty. Hypothesis, not fact: the data likely belongs to the Greater Grand Rapids affiliate (moderate analytic confidence). The domain mix, the Michigan university domain and the document reported by DysruptionHub all point that way.
Why it stands out this week. The named affiliate and the domain evidence differ. Federated non-profits share a brand but have separate networks, so notification and press responses depend on identifying whose data is exposed.
4 · Southeastern Oklahoma State University (listed by Interlock)
HIBR entry: Southeastern Oklahoma State University on HaveIBeenRansom
What happened. The university closed its campus for three days after a cyber incident at the end of July. Interlock listed it on 19 August, claiming student and employee records, including Social Security numbers. On 10 September the university told KXII that "an unauthorized actor gained access to some of our computer systems and may have acquired copies of certain files", and that it had mailed notification letters. HIBR indexed the data on 18 October.
Scale. 9,249,476 total records. Separate file-type counts: CSV 6,095,748, JSON 1,980,785, spreadsheets 1,440,300, databases 16,585. These do not reconcile with the total and must not be added. HIBR also lists 23 email files. 1,593,605 records (17.23%) contain an email address.
What the data contains. In the student.se.edu records we read, the files include user-account exports named bbusersall, orientation enrolment lists, in-room class rosters and a mid-term grades report for student athletes. The most common fields are username, first and last name, personal email, home phone, city, state and ZIP code, course, term, instructor and credit hours. Most dates fall in 2020–2021, and the latest is 3 May 2026. The Social Security numbers come from Interlock's description; the fields we read do not prove or disprove them.
Corporate vs Personal. Institutional addresses make up 66.16% of email-bearing records and personal addresses 33.84%. adventure-works.com is the fictional company domain in Microsoft's sample databases, an artefact of test data.
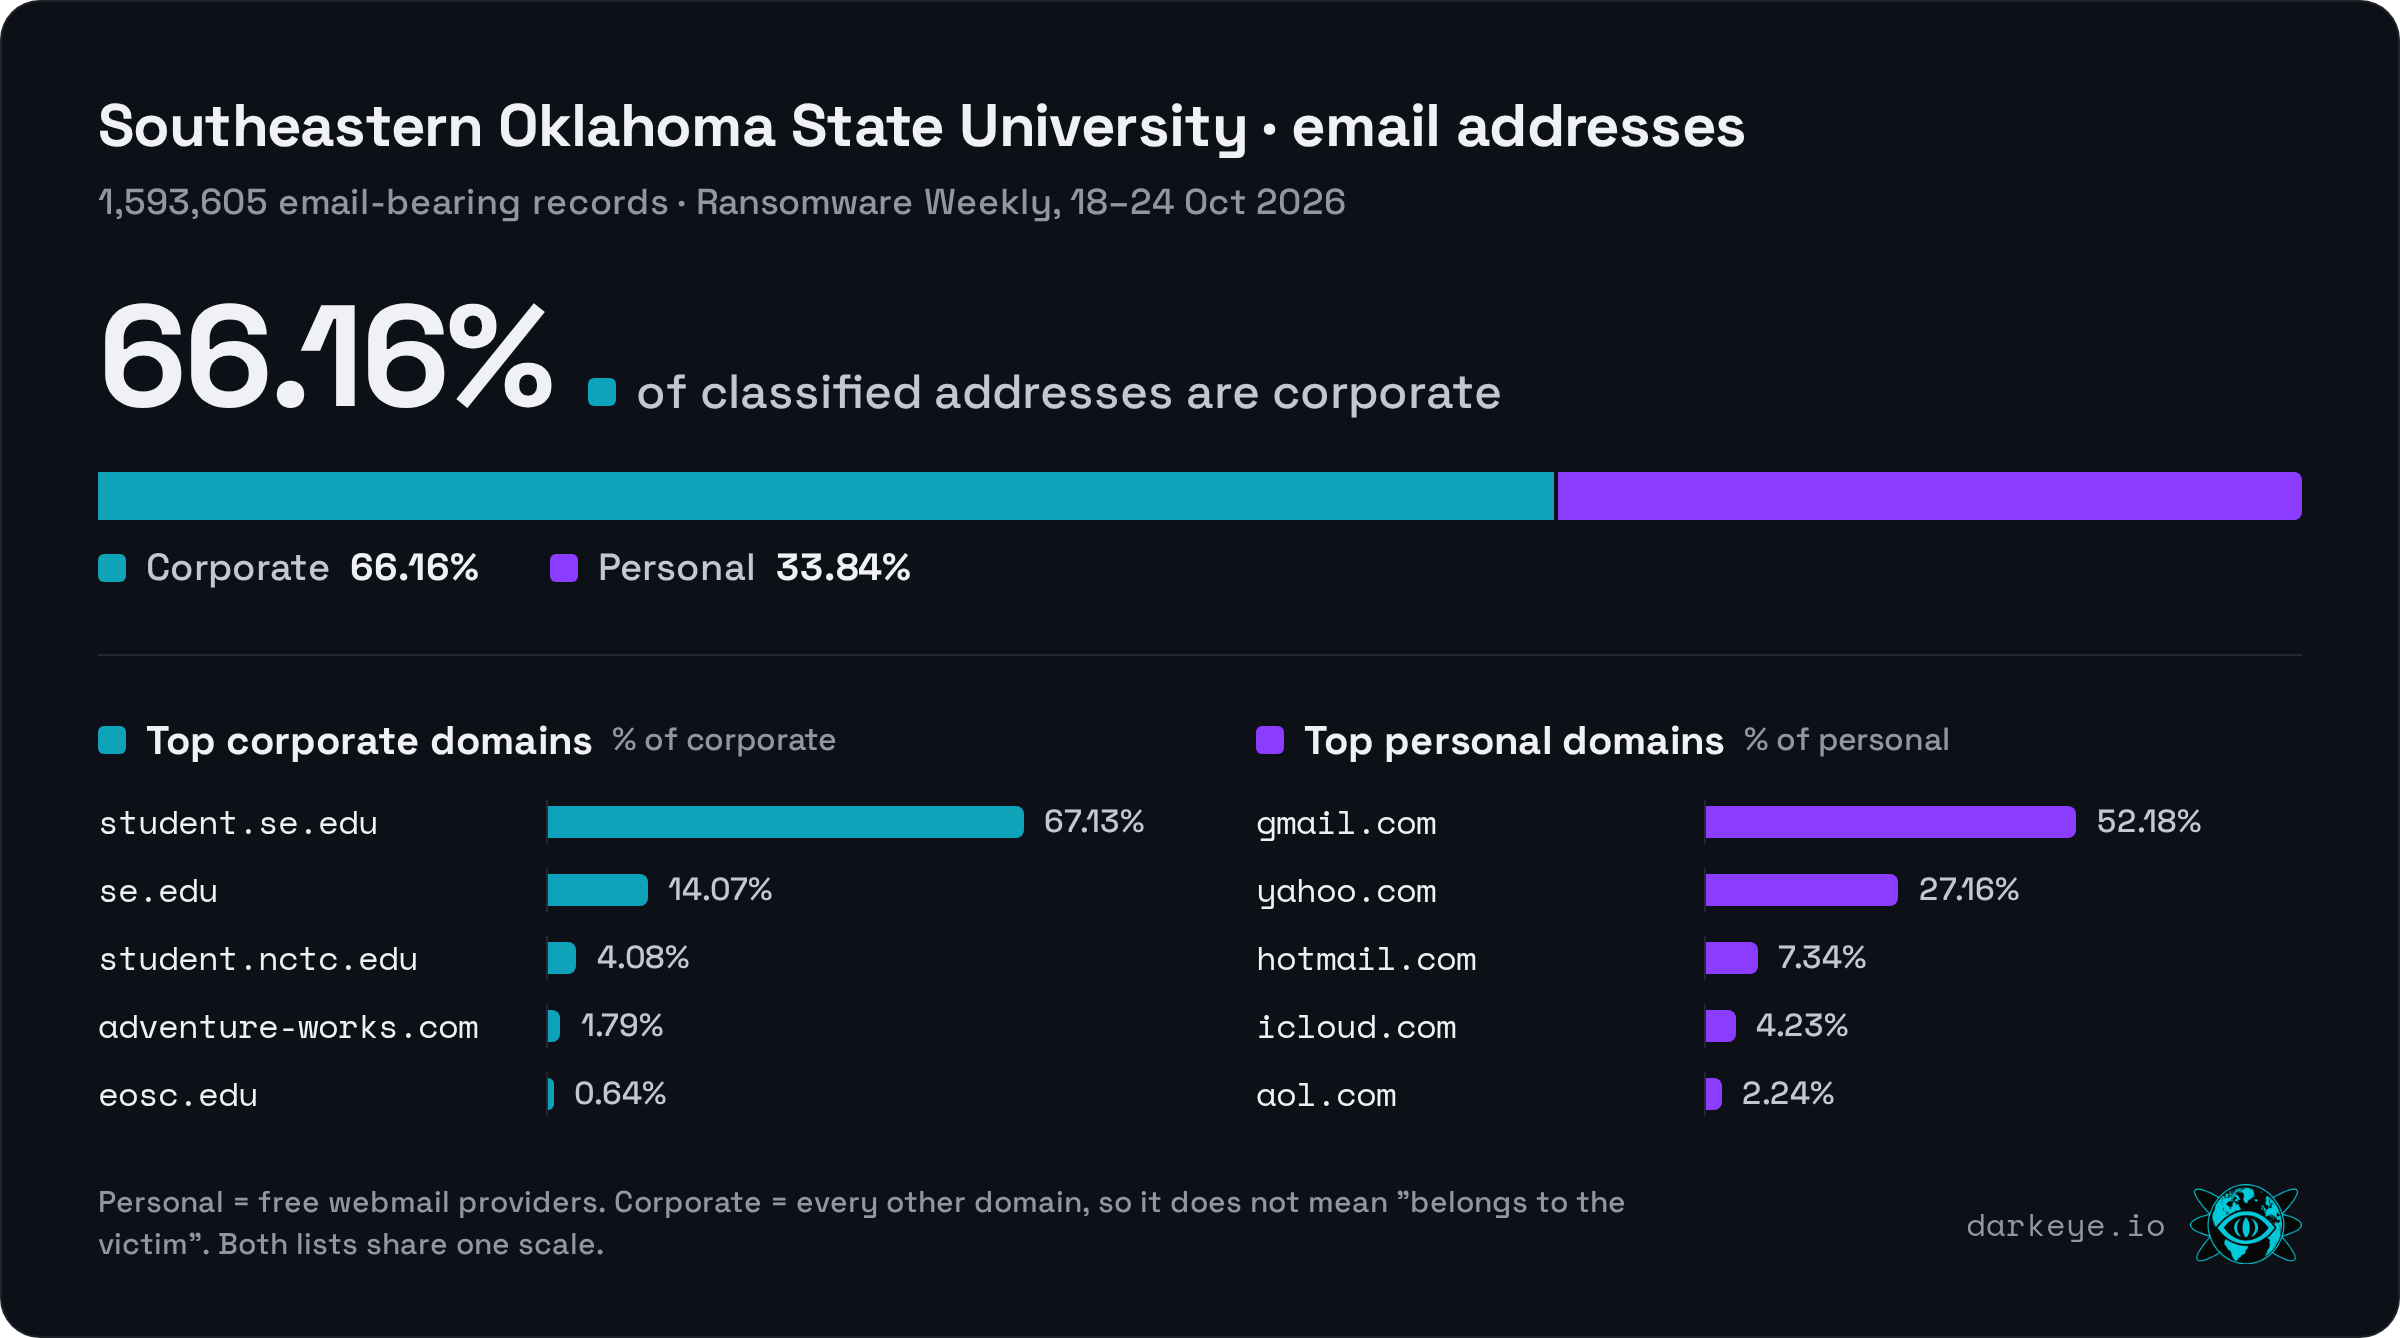
| Institutional domain | % of corporate | Personal domain | % of personal |
|---|---|---|---|
| student.se.edu | 67.13% | gmail.com | 52.18% |
| se.edu | 14.07% | yahoo.com | 27.16% |
| student.nctc.edu | 4.08% | hotmail.com | 7.34% |
| adventure-works.com | 1.79% | icloud.com | 4.23% |
| eosc.edu | 0.64% | aol.com | 2.24% |
Attribution confidence: 100/100 (high). se.edu and its student subdomain dominate the corporate class (40 of 40), and organisation labels appear in the content (15 of 15).
Why it stands out this week. Rosters, grades and home contact details make enrolment, financial-aid or athletics impersonation convincing. Hypothesis, not fact: partner-institution records are one explanation for the other college domains; confidence is low without corroboration.
Also indexed this week
The same Telegram channel re-posted several files whose names, descriptions or public reporting link them to ShinyHunters, which runs its own leak site. These unranked cases all remain claims: msgsports.com (19,583,995 records, 76/100), a file named for Alcon (17,656,014 records; attribution not computable), Berkadia (8,021,638 records, 76/100), JCPenney (1,554,726 records, 62/100) and a Neiman Marcus file that the post itself describes as the 2024 dataset (246,240,071 records, 27/100).
What they have in common
- Rows are not people: the sampled MAG rows are email-open events and Thermos records resemble PLM account tables. Use record context to interpret volume.
- Domain matching needs interpretation: MAG's automated score used a misparsed file label; Goodwill's sampled records point towards another affiliate.
- Links to extortion claims require file-level assessment: we include the MAG-labelled Telegram file on a hypothesised FulcrumSec link, with moderate analytic confidence, not verified provenance. It and five ShinyHunters-linked reposts became searchable this week; their posting dates precede this indexing window.
What defenders can do
- Iterable and other marketing platforms (MAG): search your public JavaScript and mobile apps for marketing-platform API keys, rotate any that are exposed, and give client-side keys the narrowest scope the platform allows. Watch for phishing that cites real campaign or booking details.
- PTC Windchill and FlexPLM (Thermos): if you run either, check patch status for CVE-2026-12569, review Windchill access logs for bulk exports from internet-facing servers, and audit reseller and partner accounts in WTUser.
- Federated organisations (Goodwill): keep a current list of every affiliate's domains and check leaked data against it before notifying or commenting publicly.
- Universities (Southeastern Oklahoma State University): warn students about financial-aid phishing citing real courses, remove sample-data databases from production shares and check exports to partner colleges.
Is your company — or one of your suppliers — in a ransomware leak? Search HaveIBeenRansom for free · Monitor your domains with HIBR for business
DarkEye Threat Research · Data: HaveIBeenRansom · Indexing methodology peer-reviewed in MDPI Electronics · Attribution confidence is a heuristic estimate (method v2.0), not a formal attribution.
Spotted an error, or represent an organisation named here? Send us a correction and we will add it to the post.
Darkeye Research Team
JuanmaTracking ransomware crews, breach disclosures and the tooling that matters — field notes from the Darkeye desk.
Intel briefing
Get breach reports before they trend
Ransomware intel and breach disclosures in your inbox. Signal only, no noise.
Read next //
Breaches Weekly, 11–17 Oct 2026: 236M Manchester Airport Rows, 66.7M Loozap Records
Claimed leaks indexed 11–17 Oct 2026: Manchester Airports Group (236.1M), Loozap (66.7M) and Airtel (42.1M). None is independently confirmed.
Keep investigating //
Discussion (0)
Sign in to join the discussion
Share your take with the Darkeye community.
No comments yet. Be the first to weigh in.